AVAILABLE FOR RED TEAM & SECURITY ENGAGEMENTS
Top 6% Globally on TryHackMe
Giza, Egypt (UTC+3)

Omar Adel Mahmoud Penetration Tester & Security Researcher

Offensive cybersecurity specialist focused on practical adversary emulation, network pivoting, Active Directory attack paths, and mobile application instrumentation. Dedicated to identifying deep architecture-level vulnerabilities and translating technical attack vectors into actionable remediation blueprints.

Focus 01
Network Pivoting
Tunneling & Exploitation
Focus 02
Active Directory
Kerberos & ACL Graphs
Focus 03
Android Pentest
Frida & ADB Hooking
Focus 04
Web & API
OWASP Top 10 / Logic
View Certifications Vault Orion Scanner Project ↗
Tactical Telemetry
Verified
TryHackMe Standing Top 6% Global
Active Certifications 7 Credentials
Completed Milestones 5 Certified
In Flight (Active Study) 2 In Progress
DEPI Track Duration 159 Contact Hours
MYSQL ACCELERATED REPOSITORY

Dynamic Certifications Vault

Live database-driven repository of formal offensive security certifications, network engineering accreditations, and defensive analysis credentials.

CRTOM (Certified Red Team Operations & Movement)
IN PROGRESS
Red Team Leaders
Cohort: 2026 0 views

CRTOM (Certified Red Team Operations & Movement)

Adversary emulation, Active Directory attack graphs, Kerberoasting, AS-REP roasting, lateral movement tactics, defense evasion techniques, and command & control (C2) operational security.

Verify Credential ↗
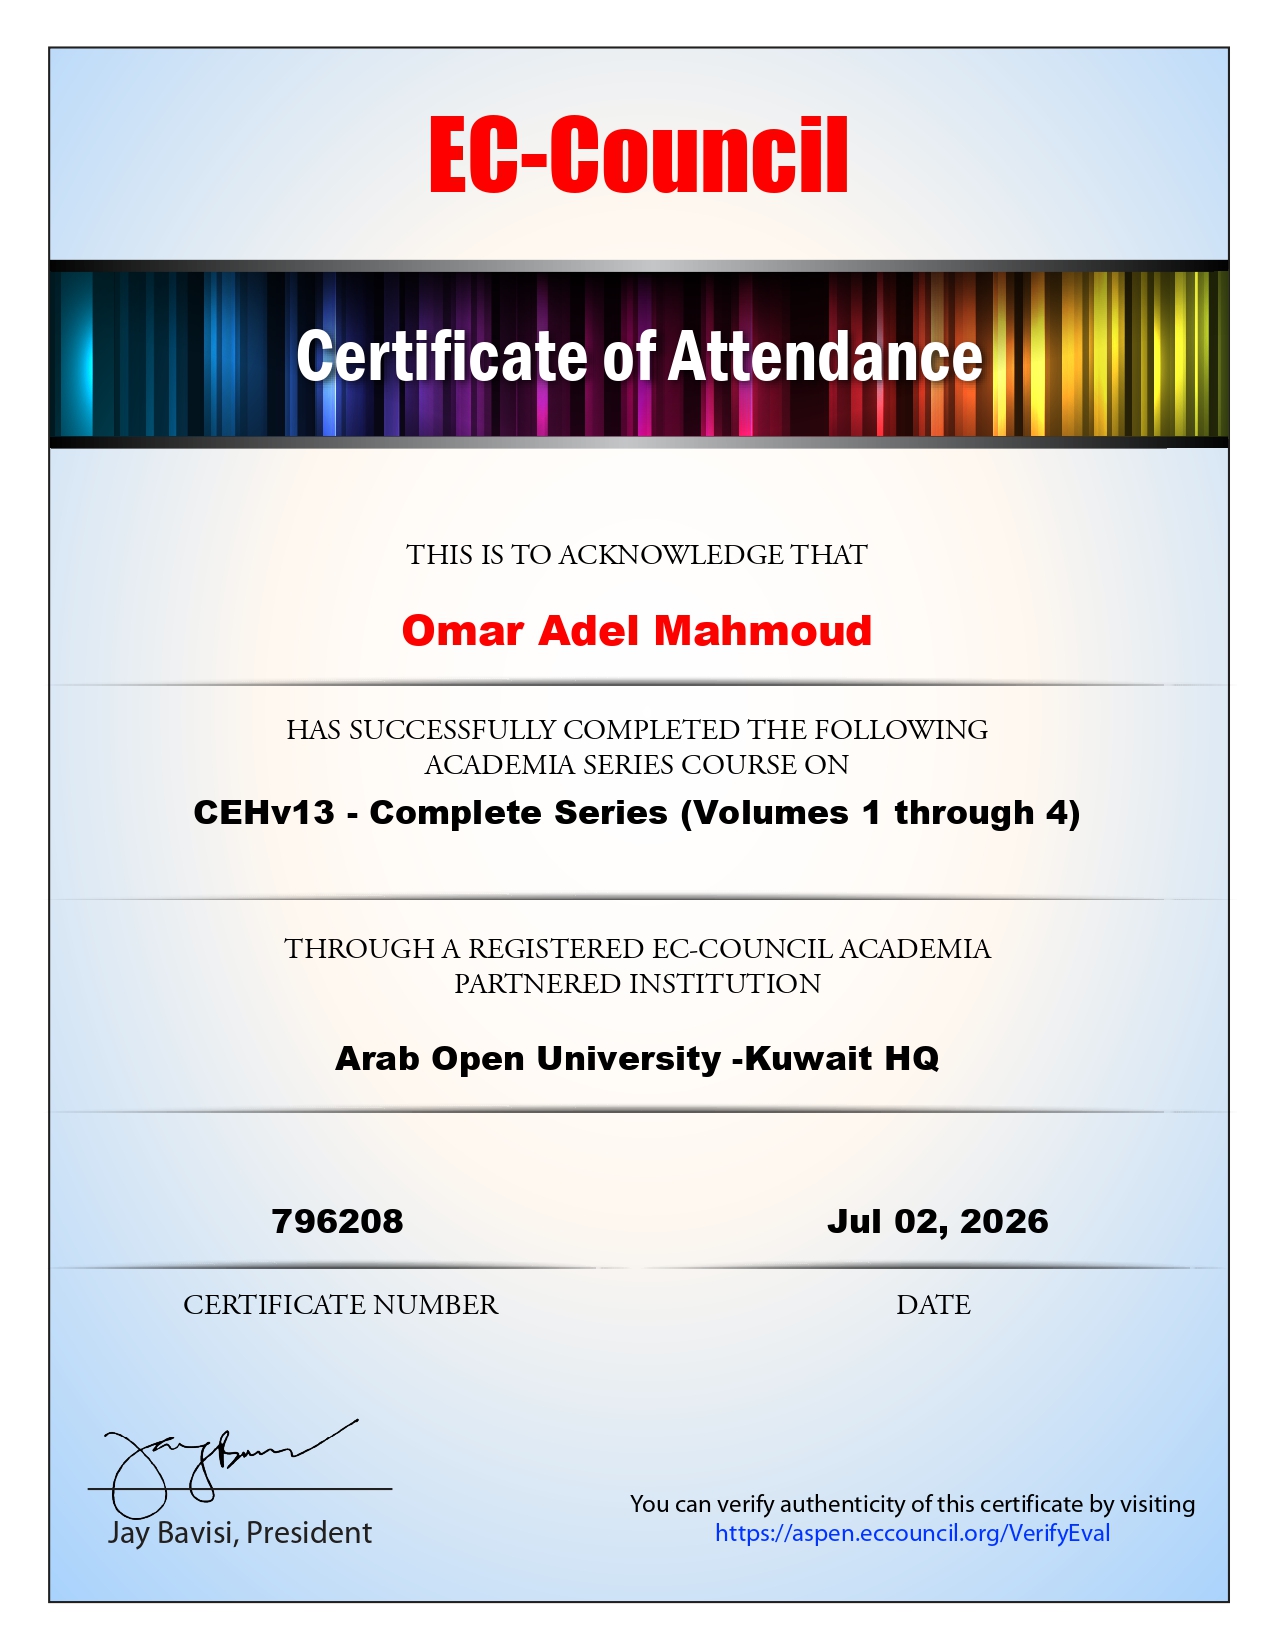
EC-Council CEH v13 (Certified Ethical Hacker)
IN PROGRESS
EC-Council
Cohort: 2026 0 views

EC-Council CEH v13 (Certified Ethical Hacker)

Comprehensive ethical hacking curriculum covering advanced reconnaissance, network/system exploitation, and web application security, integrated with AI-driven ethical hacking workflows. Evaluates defensive countermeasures, vulnerability analysis, and attack vectors across on-premise, cloud, mobile, and IoT environments.

Verify Credential ↗
INE eJPTv2 (eLearnSecurity Junior Penetration Tester)
COMPLETED
INE Security
Cohort: 2024-05 2 views

INE eJPTv2 (eLearnSecurity Junior Penetration Tester)

Practical hands-on assessment covering internal network reconnaissance, dynamic network routing & pivoting, Linux/Windows privilege escalation, manual web application exploitation, and formal remediation reporting.

Verify Credential ↗
CLLMSP (Certified Linux & Linux Security Professional)
COMPLETED
Red Team Leaders
Cohort: 2024-03 0 views

CLLMSP (Certified Linux & Linux Security Professional)

Deep-dive Linux system hardening, kernel auditing, process namespace isolation, PAM security configurations, iptables/nftables firewall administration, and secure server deployment.

Verify Credential ↗
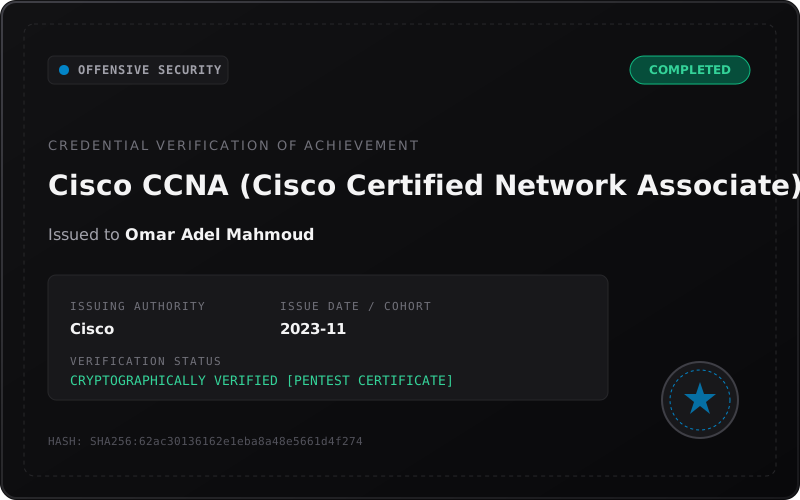
Cisco CCNA (Cisco Certified Network Associate)
COMPLETED
Cisco
Cohort: 2023-11 0 views

Cisco CCNA (Cisco Certified Network Associate)

Enterprise network architecture, IPv4/IPv6 routing protocols (OSPF), VLAN trunking & segmentation, Access Control Lists (ACLs), NAT, and core network security protocols.

Verify Credential ↗
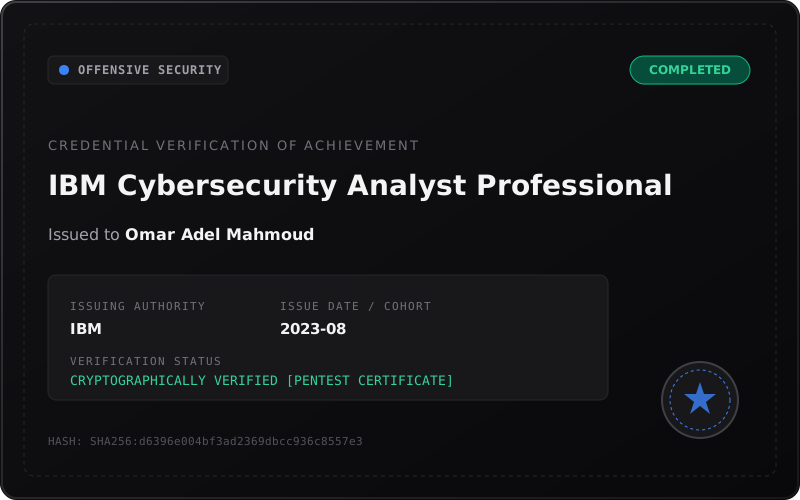
IBM Cybersecurity Analyst Professional
COMPLETED
IBM
Cohort: 2023-08 0 views

IBM Cybersecurity Analyst Professional

SIEM log telemetry, intrusion detection systems (IDS/IPS), incident response lifecycle management, network packet analysis with Wireshark, and endpoint threat hunting.

Verify Credential ↗
Graduation Capstone & Offensive Architecture
Arab Open University Graduation Project

Orion: Automated Vulnerability Scanner & Attack Graph Engine

Arab Open University Graduation Project: Advanced offensive security automation platform that conducts multi-vector vulnerability scanning, constructs dynamic attack graph models to trace lateral movement possibilities, and generates AI-assisted context-aware remediation playbooks. Engineered with asynchronous task queues and containerized microservices.

Vector Scanning
Dynamic Reconnaissance

Automated service enumeration, port auditing, and banner grabbing.

Attack Graphs
Lateral Path Modeling

Constructs dependency graphs to visualize privilege escalation chains.

Remediation
AI-Assisted Hardening

Synthesizes targeted defense playbooks and remediation scripts.

Engineered With
FastAPI React.js Celery Redis Docker PostgreSQL Nmap NetworkX Graphviz
orion-engine://attack-graph-trace
ACTIVE SESSION
# Initiating Automated Multi-Vector Scan
[+] Target: 10.10.110.0/24 (Subnet Ingestion)
[+] Discovered: 14 Live Hosts | 38 Open Ports
[!] Vulnerability Detected: CVE-2021-44228 (Log4j on Port 8080)
[!] Lateral Path Found: Host-03 -> Kerberos Unconstrained Delegation
Shortest Exploitation Chain
WEB-01 → RCE (Log4j) → DB-SQL → DOMAIN ADMIN
[+] Attack Graph Calculated: 3 Critical Pivots
[*] AI Remediation Dispatch: 2 Patch Playbooks Generated
Asynchronous Celery Pipeline Redis Broker: Connected
OFFENSIVE FIELD ENGAGEMENTS & INTERNSHIPS

Practical Experience Timeline

Track record of applied offensive cybersecurity training, real-world infrastructure assessments, mobile application pentesting, and full-stack software development.

Offensive Security Trainee

Active Directory & Mobile Security
Digital Egypt Pioneers Initiative (DEPI)
2024 (159 Intensive Hours)
  • ▸ Mastered Active Directory exploitation chains: Kerberoasting, AS-REP Roasting, Pass-the-Hash, and BloodHound attack path mapping.
  • ▸ Conducted dynamic Android penetration testing using Frida instrumentation, ADB debugging, APK reverse-engineering (JADX), and SSL Pinning bypass.
  • ▸ Performed comprehensive REST API vulnerability assessments following OWASP API Security Top 10 standards.

Penetration Tester Trainee

Infrastructure & Web Pentesting
CodeAlpha
2023 - 2024
  • ▸ Executed network penetration testing engagements utilizing Nmap for port reconnaissance and service enumeration.
  • ▸ Exploited system vulnerabilities using Metasploit Framework and developed custom proof-of-concept exploit scripts.
  • ▸ Performed manual web application security testing using Burp Suite Professional to identify injection flaws and auth bypasses.

Cyber Week Plus Bootcamp & CTF Competitor

Offensive Operations & CTF
Xpand CS Academy
2023
  • ▸ Participated in high-intensity capture-the-flag (CTF) challenges focusing on reverse engineering, web exploitation, and cryptography.
  • ▸ Enhanced binary exploitation fundamentals and offensive methodology in simulated hostile enterprise environments.

Front-End Web Developer

Full-Stack Development
Mostaqel (Freelance)
2022 - 2023
  • ▸ Architected responsive, zero-latency user interfaces using React.js, Tailwind CSS, and modern JavaScript standards.
  • ▸ Gained deep foundational insight into modern web applications, client-server architectures, and DOM security, empowering web penetration testing capabilities.
ARSENAL & RECONNAISSANCE STACK

Offensive Tooling Matrix

Categorized offensive security tooling, exploitation frameworks, and automation scripts utilized during blackbox, greybox, and red team operations.

Network & Infrastructure
Nmap ADVANCED

NSE scripting, stealth SYN scanning, service fingerprinting

Metasploit PROFICIENT

Payload generation, handler staging, post-exploitation modules

Wireshark ADVANCED

Deep packet inspection, pcap traffic analysis, credential discovery

Nessus PROFICIENT

Automated vulnerability scanning, compliance auditing

Web Application & API
Burp Suite Pro EXPERT

Repeater, Intruder, Match/Replace rules, Collaborator, extensions

OWASP ZAP PROFICIENT

Active scanning, spidering, automated security regression

Postman ADVANCED

API authorization tampering, mass assignment fuzzing, rate-limit testing

SQLMap ADVANCED

Blind time-based, error-based SQL injection automation

Active Directory & Red Teaming
BloodHound ADVANCED

SharpHound ingest, shortest path analysis, ACL abuse graphs

Impacket ADVANCED

secretsdump, wmiexec, psexec, GetNPUsers, ticket extraction

Mimikatz PROFICIENT

LSASS memory extraction, Pass-the-Hash, Golden Ticket forging

CrackMapExec ADVANCED

Network credential validation, SMB/WinRM spraying, share crawling

Mobile / Android Pentesting
Frida ADVANCED

Dynamic instrumentation, runtime hooking, SSL Pinning bypass

ADB ADVANCED

Device debugging, shell execution, backup extraction, activity inspection

JADX-GUI PROFICIENT

APK decompilation, source code audit, hardcoded secret discovery

MobSF PROFICIENT

Static & dynamic automated mobile security framework analysis

Scripting & Operations
Python ADVANCED

Custom exploit development, automation, socket programming, Scapy

Bash ADVANCED

Reconnaissance automation, Linux pipe chaining, log parsing

PowerShell PROFICIENT

Living-off-the-land techniques, WMI queries, script automation

Linux Hardening ADVANCED

Debian/Ubuntu/Kali administration, permissions, systemd isolation

OFFENSIVE UTILITIES & TOOL DEVELOPMENT

Technical Projects & Toolkits

Open-source exploitation scripts, automation tools, and security research implementations.

frida-droidsec FEATURED

Frida-DroidSec: Dynamic Android Pentest Toolkit

Modular Frida instrumentation suite engineered for mobile application security assessments. Automates SSL Pinning bypasses across OkHttp3/TrustManager, bypasses anti-root and emulator detection mechanisms, and extracts sensitive cryptographic keys from runtime process memory.

Frida JavaScript Python ADB
ad-specter FEATURED

AD-Specter: Active Directory Attack Path Enumerator

Offensive Active Directory tooling designed to automate the discovery of misconfigured Kerberos delegation, ACL abuse paths, and unconstrained delegation chains. Integrates with BloodHound datasets to highlight quick-win exploitation routes for red teams.

Python Impacket BloodHound API PowerShell
netpivot-agent

NetPivot: Automated Port Forwarding & Pivoting Agent

Lightweight offensive networking utility built for seamless internal network pivoting during engagements. Implements encrypted SOCKS5 tunneling, dynamic port forwarding, and stealth traffic masquerading.

Go Bash Linux Netfilter SOCKS5
OFFENSIVE RESEARCH & EXPLOITATION DOCUMENTATION

Security Writeups & Exploitation Deep-Dives

Technical post-mortems, CTF walkthroughs, Active Directory attack paths, and mobile runtime analysis authored by Omar Adel Mahmoud.

View All Writeups (4) →
Direct Communications Channel

Engage for Security Audits & Roles

Available for penetration testing contracts, full-time offensive security roles, and vulnerability assessments.

Primary Email
omarsilvawa@gmail.com
Direct / WhatsApp
+20 1101848363
Location & Timezone
Giza, Egypt • Eastern European Time (UTC+2 / UTC+3)